
inSight Security Monitoring
Municipal police departments cannot afford to discover suspicious activity only after systems are compromised. Without centralized security monitoring, important events occurring across servers, workstations and critical applications can remain unnoticed or become buried among thousands of routine system messages.
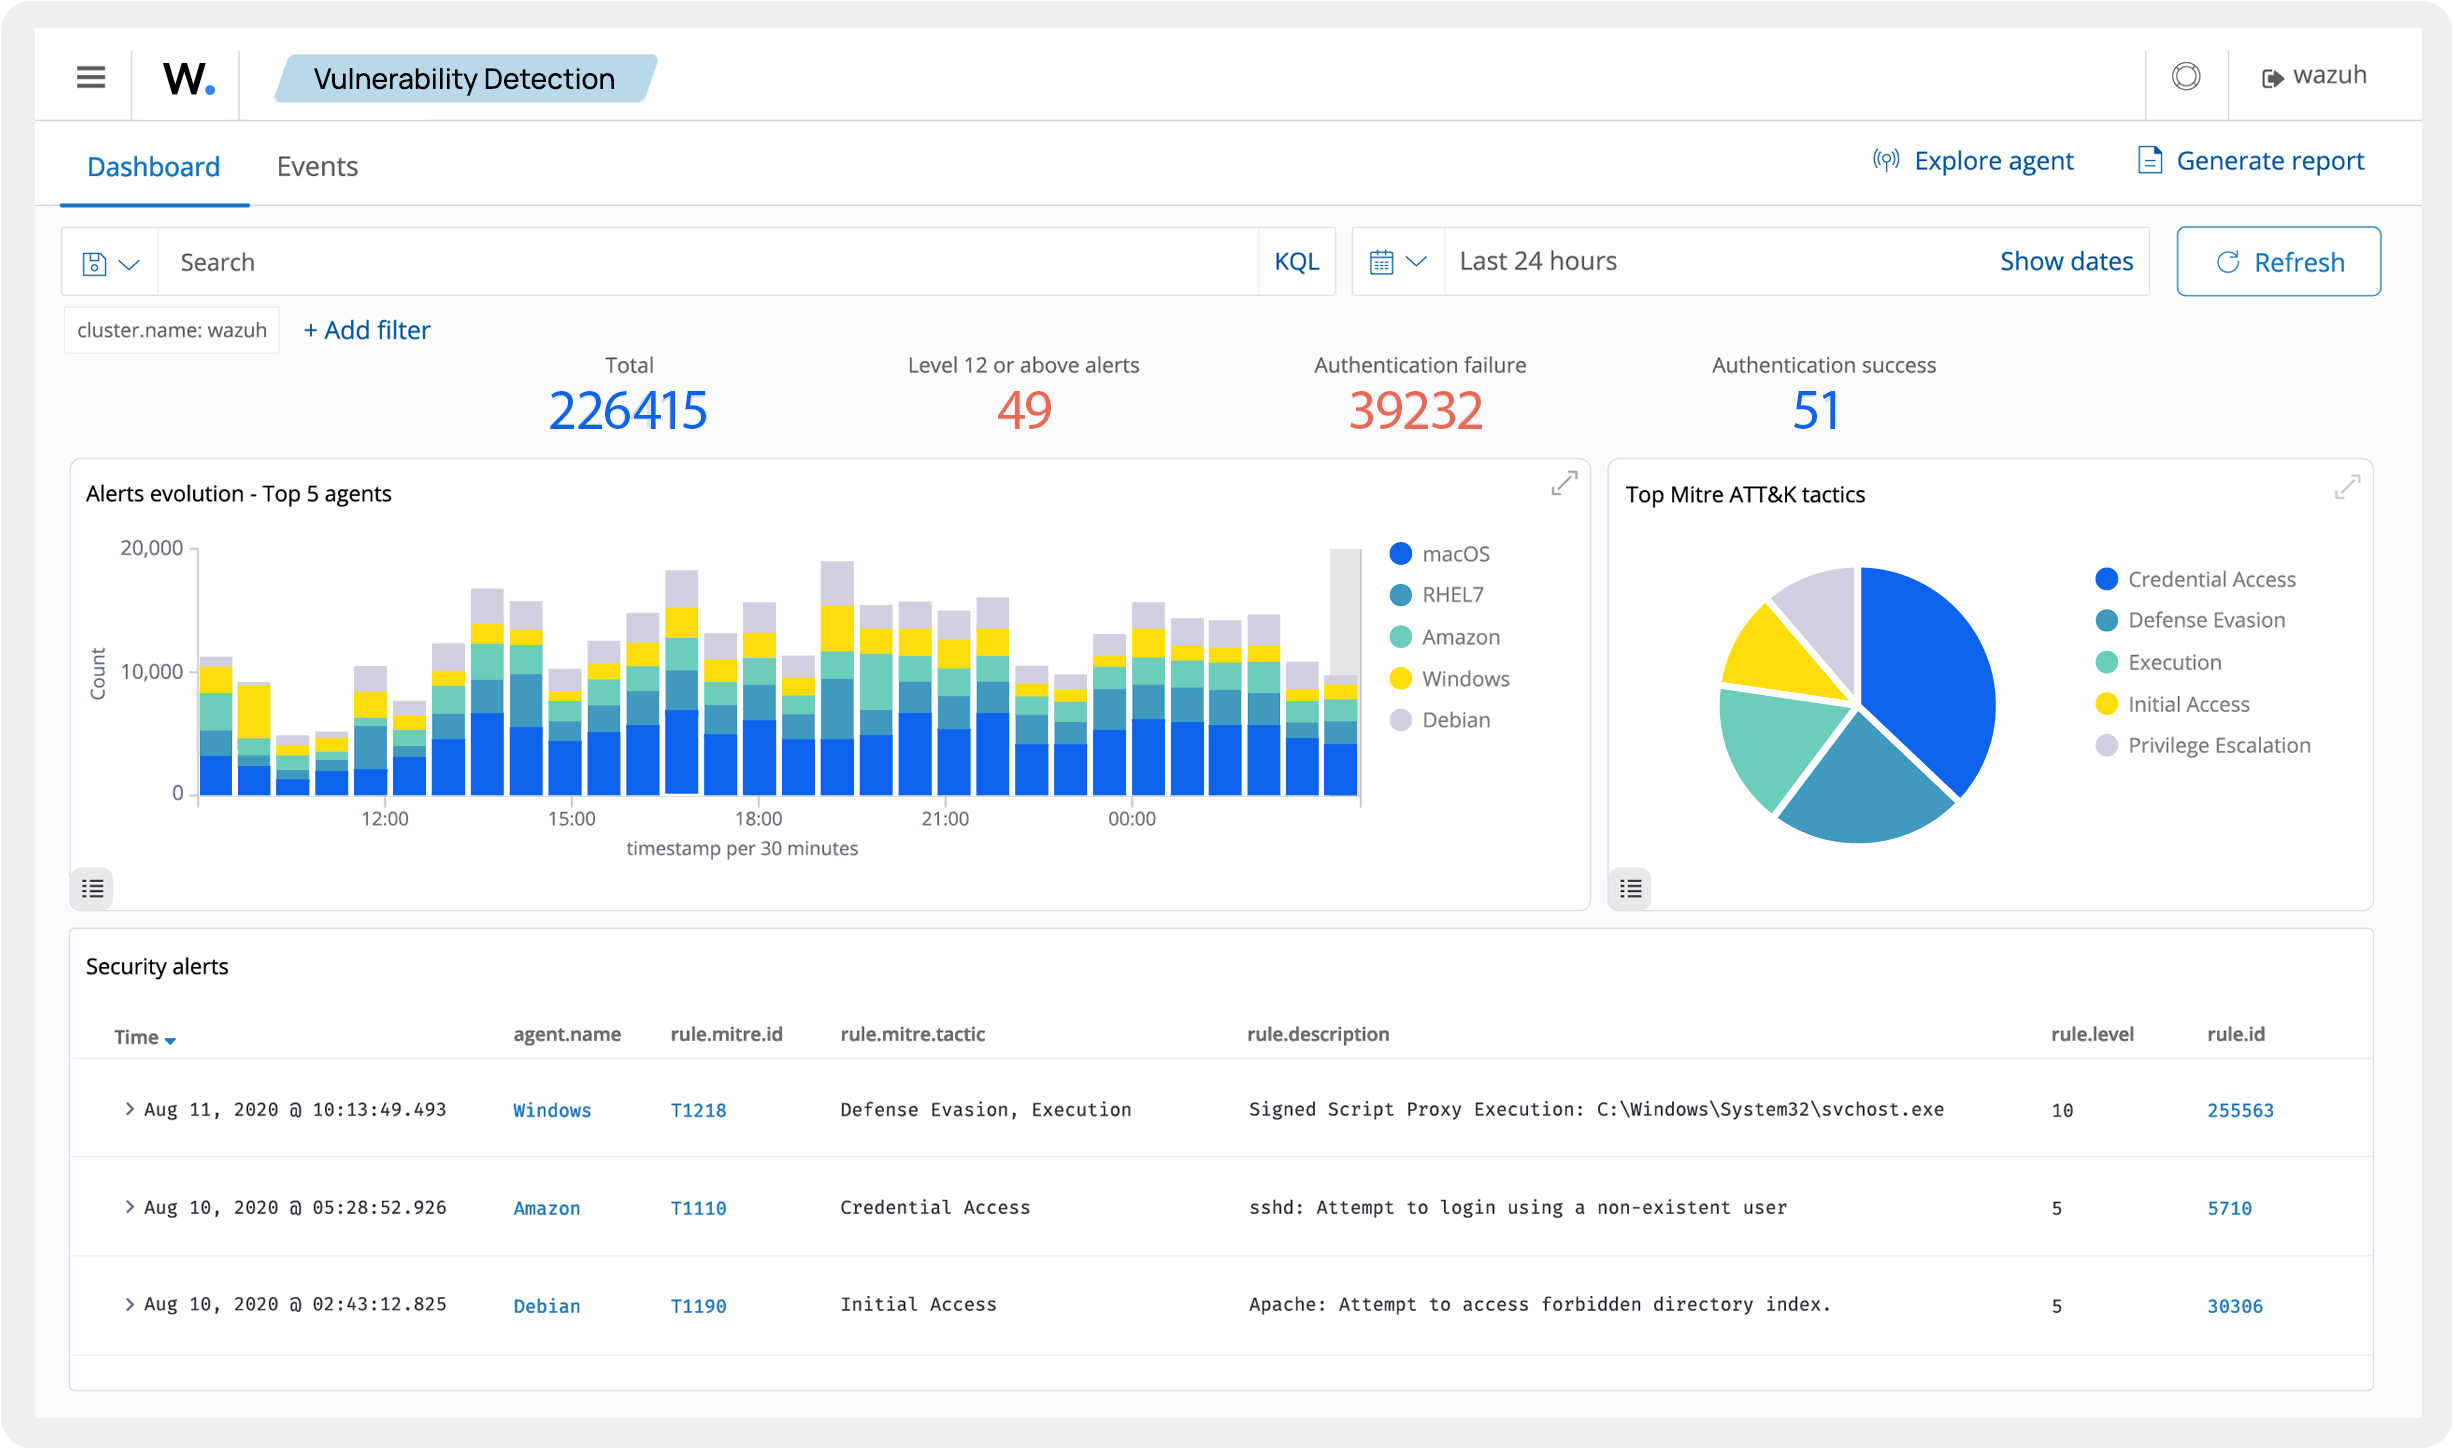
inSight Security Monitoring provides continuous security visibility across municipal technology environments, helping agencies identify suspicious activity, investigate security events and maintain evidence of ongoing security oversight.
The service can include:
Continuous security monitoring of Windows and Linux systems
Centralized collection and analysis of security events
Authentication and account activity monitoring
Detection of suspicious processes, files and system behavior
File and configuration integrity monitoring
Malware and threat-indicator detection
Security configuration and policy monitoring
Correlation and prioritization of security events
Investigation and escalation of significant findings
Recurring security and CJIS oversight reporting
Audit-ready evidence aligned with CJIS Security Policy requirements
Day-to-day and audit support from our trusted US-based technical team
CJIS security requirements extend beyond deploying antivirus software or retaining logs. Agencies must continuously monitor systems, identify potentially harmful activity, review security events and demonstrate that security controls remain effective.
How inSight Vulnerability Management Supports CJIS
inSight Vulnerability Management is designed to support controls including:
RA-5 — Vulnerability Monitoring and Scanning
RA-5(2) — Update Vulnerabilities to Be Scanned
RA-5(5) — Privileged Access
SI-2 — Flaw Remediation
CM-8 — System Component Inventory
CA-7 — Continuous Monitoring
RA-3 — Risk Assessment
The service supports these requirements but does not independently guarantee CJIS compliance. Compliance also depends on agency policies, asset ownership, remediation decisions, access controls, documentation and coordination with the applicable CJIS Systems Agency.
ACT NOW. Detect suspicious activity before it becomes a security incident.
Features
-
inSight Vulnerability Management assesses authorized systems from within the customer’s trusted network environment using an encrypted site-to-site VPN or an optional on-site scan engine.
Internal assessment can include:
Windows and Linux servers
Domain controllers and directory services
User workstations and administrative systems
Firewalls, switches and wireless infrastructure
VMware and other virtualization platforms
Storage, backup and application servers
Printers, cameras and other supported network devices
Systems supporting CJIS and public-safety workflows
Authenticated scanning uses authorized credentials where appropriate to inspect installed software, missing updates, security configurations and other conditions that cannot reliably be identified through an unauthenticated network scan.
This supports CJIS vulnerability monitoring, privileged scanning and system-component inventory requirements, including RA-5, RA-5(5), CM-8 and CA-7.
-
Internal scanning identifies risks reachable from trusted networks. External assessment identifies what a potential attacker can reach from the public Internet.
inSight Vulnerability Management assesses authorized public-facing assets for conditions such as:
Exposed network services
Outdated or vulnerable software
Weak encryption protocols and certificates
Insecure remote-access services
Unexpected administrative interfaces
Misconfigured web applications and services
Changes to the municipality’s external attack surface
Internal and external assessments provide complementary views of risk. Neither should be treated as a substitute for the other.
-
A vulnerability management program is only effective when the agency knows which systems should be assessed.
Trestle reconciles scan results against available authoritative sources, which may include:
Active Directory
inSight Monitoring
Endpoint security platforms
VMware and virtualization inventory
DHCP, ARP and switch forwarding information
Firewall objects and network documentation
Existing municipal asset records
This process helps identify:
Systems missing from the formal inventory
Devices that could not be reached during a scan
Unsupported or obsolete operating systems
Unmanaged endpoints
Unknown network devices
Retired assets that remain connected
Discrepancies between operational and documented inventory
This strengthens the relationship between vulnerability management and CJIS system-component inventory requirements under CM-8.
-
Automated scanners can produce hundreds or thousands of findings. They cannot independently determine which vulnerabilities create the greatest operational risk to a police department.
Trestle reviews and prioritizes findings using factors such as:
Technical severity and CVSS score
Evidence of active exploitation
Internet exposure
Access to Criminal Justice Information
System criticality
Availability of patches or mitigations
Existing security controls
Operational impact of remediation
Age of the vulnerability
Whether the finding has been validated
This allows municipalities to focus limited technical resources on the vulnerabilities most likely to affect public safety, security or CJIS compliance.
-
Vulnerability management does not end when a scan report is delivered.
inSight Vulnerability Management maintains a structured remediation process that documents:
Affected system and vulnerability
Technical severity and operational risk
Recommended corrective action
Assigned responsible party
Target remediation date
Current remediation status
Technical or operational dependencies
Approved exceptions
Compensating controls
Rescan results and closure evidence
Remediated findings are rescanned whenever practical to verify that the vulnerability is no longer present.
Findings that cannot be immediately corrected remain visible until resolved, mitigated or formally accepted. This supports CJIS RA-5 vulnerability monitoring and SI-2 flaw-remediation tracking.
-
The vulnerabilities affecting municipal systems continually change as researchers, vendors and government agencies disclose new security weaknesses.
Trestle maintains current scanning content and adjusts the assessment program when:
New critical vulnerabilities are announced
A vulnerability is known to be actively exploited
Significant new systems are deployed
Major operating-system or application changes occur
New attack techniques affect existing infrastructure
Security advisories identify potentially vulnerable products
Where appropriate, Trestle can perform targeted out-of-cycle assessments to determine whether a newly disclosed vulnerability affects the customer environment.
This supports RA-5(2), which requires agencies to update the vulnerabilities being assessed as new vulnerabilities are identified.
-
inSight Vulnerability Management reports are designed for action and oversight—not simply to reproduce raw scanner output.
Recurring reports may include:
Executive summary of current risk
Asset and scan-coverage statistics
Critical and high-priority vulnerabilities
Newly discovered findings
Outstanding findings by age
Remediation progress
Overdue corrective actions
Accepted risks and compensating controls
Systems that could not be authenticated or reached
Verification-scan results
Trends across reporting periods
CJIS control alignment
Technical details remain available for administrators, while concise management reporting helps police leadership and municipal officials understand exposure, progress and required decisions.
-
CJIS readiness requires agencies to demonstrate that vulnerabilities are identified, reviewed and addressed through an established process.
inSight Vulnerability Management helps maintain repeatable evidence such as:
Approved scan scope
Asset and network coverage records
Scan schedules and completion history
Authenticated-scan status
Vulnerability reports
Review and prioritization records
Remediation tickets
Exception and risk-acceptance documentation
Rescan and closure evidence
Periodic management reports
This is the difference between “we ran a scan” and “we operate a vulnerability management program.”